Cross-account VPC peering
A networking lab connecting frontend and backend VPCs across AWS accounts and regions. Terraform requests and accepts the peering connection, while route tables and security groups define which private instances can communicate.
Architecture
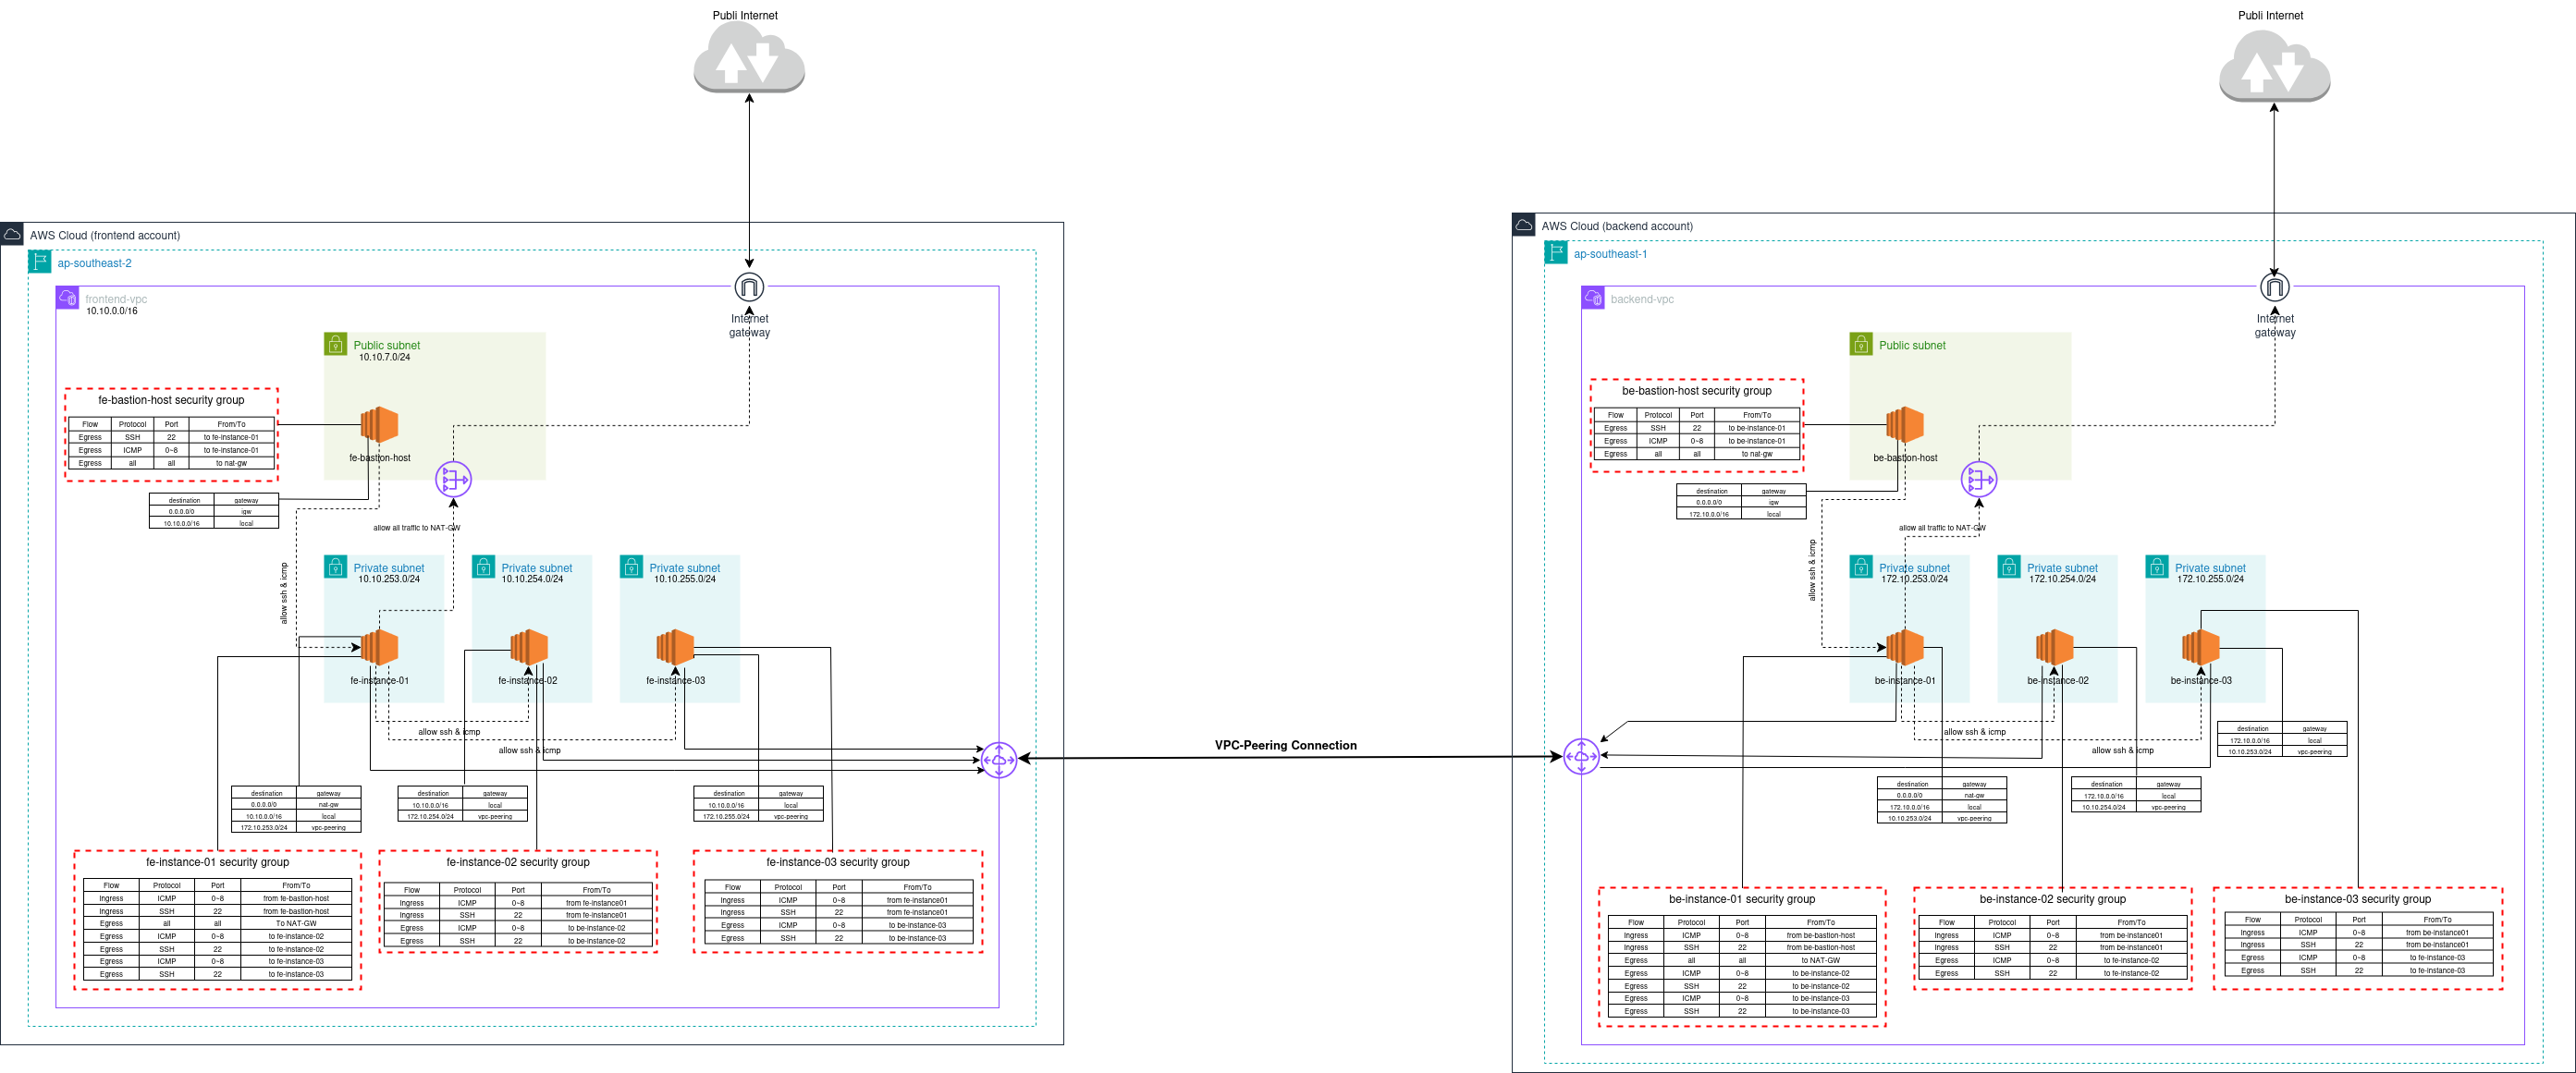
The frontend and backend each have a VPC with a public bastion subnet and private instance subnets. Two aliased AWS providers use separate account profiles. The frontend provider creates the peering request; the backend provider accepts it. Routes on both sides point selected destinations to the peering connection.
Implementation flow
Configure both accounts
Provide the frontend and backend AWS profiles and their regions. The README documents IAM permissions needed to work with VPC and peering resources.
Build the networks
Create a VPC, a public subnet, private subnets, an Internet Gateway, and a NAT Gateway on each side, along with bastion and private EC2 instances.
Request and accept peering
Use the frontend VPC as requester and identify the backend account and region. Accept the pending connection with the backend provider.
Add reciprocal routes
Associate dedicated private route tables and add peering routes for selected opposite-side destinations. The public subnet routes to the Internet Gateway.
Restrict instance paths
Use security groups for bastion access and private instance communication. Cross-account instance rules target the remote private IP address.
Verify traffic
Test ICMP and SSH along the intended paths, then inspect the instance and route table screenshots in the repository.
Connection evidence
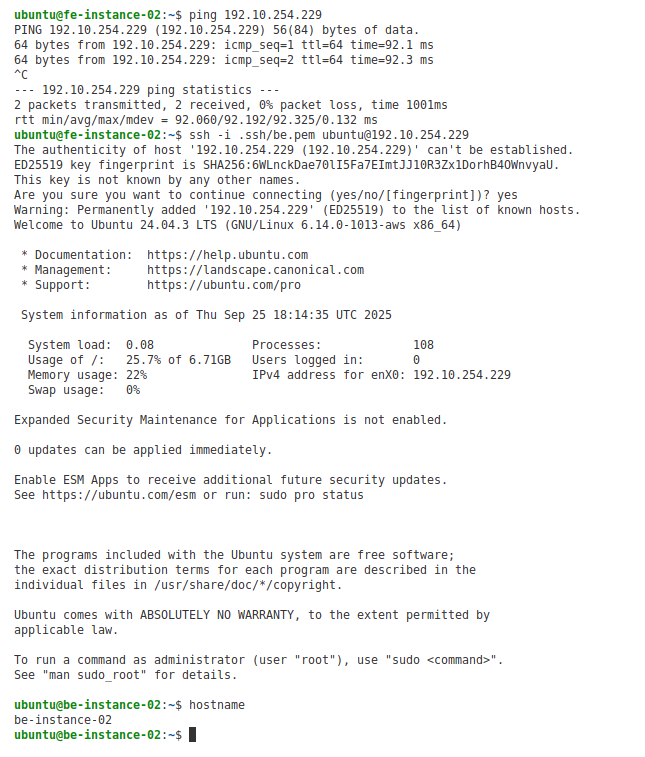
A repository capture shows fe-instance-02 pinging be-instance-02 and opening an SSH session across the peering connection. This is evidence for that tested path in the lab.
Repository notes
The Terraform uses configured AWS profiles; role creation and trust configuration are described as prerequisites rather than created in these files. The lab's bastion security groups allow SSH and ICMP from 0.0.0.0/0; narrow those rules to trusted sources before adapting the design.
Based on the vpc_peering_rolebased_across_accounts folder on GitLab. The screenshots document a lab result, not a continuously running environment.