Private EC2 access with AWS Systems Manager
A hands-on infrastructure lab for reaching EC2 instances in private subnets through Session Manager and VPC interface endpoints, without public instance IPs, a bastion host, or a NAT Gateway.
Architecture
The Terraform code builds a VPC in ap-southeast-1, with three private route tables and an EC2 instance in each subnet. The instances have no public IP addresses. IAM instance profiles grant Systems Manager permissions, while private DNS resolves SSM service names to VPC endpoints.
How the lab is built
Define the VPC and subnets
Create a
10.0.0.0/16VPC with DNS support, three subnets in separate availability zones, and route tables without an internet route.Launch private instances
Use an Ubuntu 24.04 AMI, explicitly disable public IP assignment for each EC2 instance, and attach a dedicated security group.
Assign IAM permissions
Attach the AWS managed
AmazonSSMManagedInstanceCorepolicy to an EC2 role through an instance profile.Create interface endpoints
Provision
ssm,ssmmessages, andec2messagesendpoints in all three subnets, with private DNS enabled.Limit network access
Permit outbound HTTPS from instances to the endpoint security group; the endpoint group accepts TCP 443 from the VPC CIDR. No inbound SSH rule is defined for instances.
Connect and verify
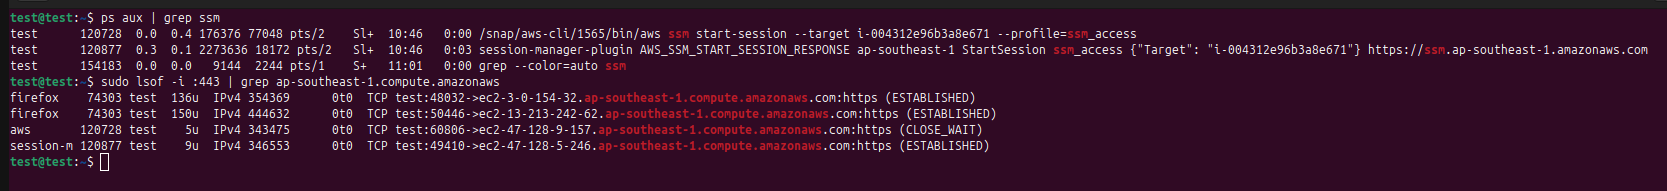
Start a Session Manager session by instance ID, then inspect the agent process and established HTTPS connections.
Connection and evidence
The repository includes terminal captures showing a Session Manager session on an instance and the AWS CLI process on the operator's host.
aws ssm start-session --target <instance-id> --profile ssm_access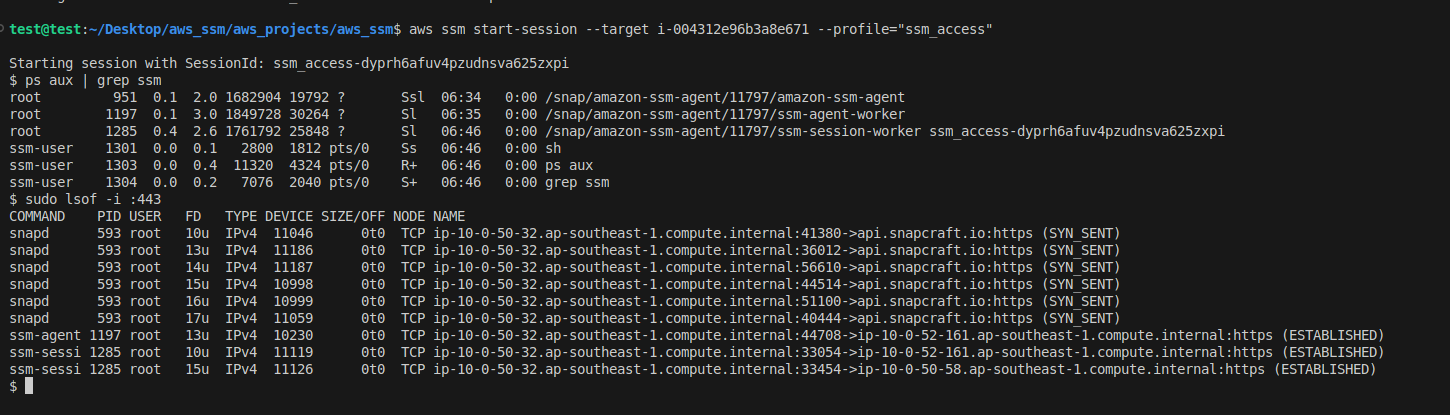
Repository notes
The Terraform files define three instances and subnets, though the README overview says two. The subnet resources also set map_public_ip_on_launch = true; each defined EC2 instance separately sets associate_public_ip_address = false. Align those settings before reusing this as a general private subnet template.
Based on the aws_ssm folder in the GitLab repository. Configuration and evidence describe this lab, not a continuously running environment.